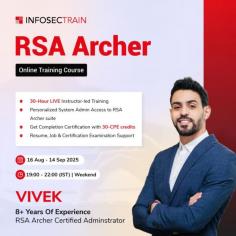
RSA Archer Training equips professionals with the skills to effectively use RSA Archer, a leading governance, risk, and compliance (GRC) platform. This training covers core modules such as risk management, compliance management, incident tracking, and audit management, enabling participants to configure workflows, analyze data, and streamline reporting. By mastering RSA Archer, learners can enhance organizational risk visibility, improve decision-making, and ensure regulatory compliance efficiently.

Thumb

0 repins 0 comments

Master the 8 domains, build a focused study plan, use official resources, and practice smart. Join study groups, take mock exams, and consider expert-led training for that extra edge. Don’t forget the endorsement process after you pass!

Thumb

0 repins 0 comments

Thumb

0 repins 0 comments

ChatGPT said: To clear the CISA exam in 2025, focus on the latest ISACA syllabus and study regularly using the official review manual and QAE (Questions, Answers & Explanations) database. Allocate 2–3 months for preparation, with extra attention on high-weight domains like Risk Management and Governance. Take practice exams, review weak areas, and manage your time effectively during the test. Consistency, understanding concepts—not memorizing—and regular revision are key to passing on your first attempt.

Thumb

0 repins 0 comments

Thumb

0 repins 0 comments

Chief Information Security Officers (CISOs) must implement robust incident response strategies to minimize damage and recover quickly from cyber threats. Key strategies include developing a clear, tested incident response plan, forming a cross-functional response team, ensuring real-time threat detection, and maintaining strong communication protocols during a breach. Regular training, threat simulations, and post-incident reviews help improve readiness. By focusing on speed, coordination, and continuous improvement, CISOs can effectively lead their organizations through security incidents while minimizing business impact.

Thumb

0 repins 0 comments

Enhance your cybersecurity skills with our Threat Hunting Training Course in Saudi Arabia, designed to equip professionals with advanced techniques to proactively detect and mitigate threats. This hands-on course covers adversary tactics, threat intelligence, and hunting methodologies using real-world tools and frameworks like MITRE ATT&CK. Ideal for SOC analysts, blue teamers, and security professionals aiming to strengthen organizational defenses and gain a competitive edge in the cybersecurity landscape.

Thumb

0 repins 0 comments

NIST Cybersecurity Framework (CSF) 2.0 and CIS Benchmarks serve different but complementary purposes in cybersecurity. NIST CSF 2.0 is a high-level risk management framework designed to help organizations identify, protect, detect, respond, and recover from cybersecurity threats. It provides a strategic approach and aligns with various industry standards. In contrast, CIS Benchmarks are detailed, prescriptive configuration guidelines aimed at securing specific technologies like operating systems, databases, and cloud environments. While NIST CSF 2.0 focuses on overall cybersecurity posture and governance, CIS Benchmarks provide actionable technical hardening steps, making them highly effective when used together.

Thumb

0 repins 0 comments

ChatGPT said: Wireshark Traffic Analysis is a powerful method for capturing and examining network packets to identify performance issues, security threats, or unusual network activity. Using Wireshark, analysts can inspect protocols, detect malicious traffic, and troubleshoot connectivity problems in real time. It is widely used for network forensics, incident response, and monitoring data flow to ensure secure communication. Mastering Wireshark Traffic Analysis helps professionals gain deep insights into network behavior and quickly respond to potential cyber threats.

Thumb

0 repins 0 comments

An Intrusion Detection System (IDS) monitors network traffic or system activities to detect suspicious behavior, policy violations, or potential cyberattacks. It analyzes data in real-time using predefined rules, signatures, or behavioral patterns to identify threats like malware, unauthorized access, or data exfiltration. When a threat is detected, the IDS generates alerts to notify administrators for further investigation. While it doesn't block attacks, it plays a critical role in early detection and incident response within an organization’s security infrastructure.

Thumb

0 repins 0 comments

Malware analysis tools are essential for identifying, examining, and understanding malicious software behavior. These tools help cybersecurity professionals detect threats, analyze malware functionality, and develop effective countermeasures. Popular tools include Wireshark for network traffic analysis, Ghidra and IDA Pro for reverse engineering, VirusTotal for scanning suspicious files, and Cuckoo Sandbox for dynamic analysis in isolated environments. By using these tools, analysts can dissect malware safely, understand its impact, and enhance system defenses against future attacks.

Thumb

0 repins 0 comments

Dynamic Host Configuration Protocol (DHCP) is a network protocol used to automatically assign IP addresses and other network configuration settings to devices on a network. When a device connects to the network, it sends a DHCP Discover message. The DHCP server responds with an Offer, providing an available IP address. The device then sends a Request to accept the offer, and the server finalizes the process with an Acknowledgment. This dynamic system simplifies network management by reducing the need for manual IP configuration and ensures devices can communicate efficiently within the network.

Thumb

0 repins 0 comments

With tools like

Thumb

0 repins 0 comments

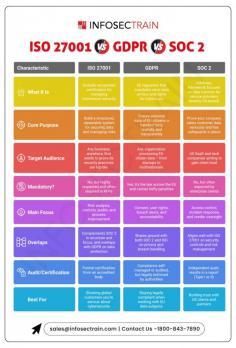
In today’s data-driven world, knowing which standard or framework applies to your business is crucial. Here's a quick comparison to help you navigate the landscape:

Thumb

0 repins 0 comments

Thumb

0 repins 0 comments

Thumb

0 repins 0 comments

Must-Know Wireshark Display Filters help cybersecurity professionals quickly analyze network traffic by isolating specific packets. These filters make it easier to detect anomalies, troubleshoot issues, and investigate potential threats. Common examples include filters for IP addresses, specific protocols, port numbers, or error types. Mastering display filters is essential for efficient network monitoring and faster incident response.

Thumb

0 repins 0 comments

Certified Ethical Hackers (CEH) use a wide range of advanced tools to identify vulnerabilities and strengthen security systems. Popular tools include Nmap for network scanning, Metasploit for penetration testing, and Wireshark for traffic analysis. Ethical hackers also rely on Burp Suite for web application security testing and John the Ripper for password cracking. These tools help CEH professionals simulate real-world cyberattacks and enhance an organization’s defense mechanisms.

Thumb

0 repins 0 comments

Thumb

0 repins 0 comments

The Linux Cheatsheet for DevOps Engineers is a handy resource that covers essential commands, shortcuts, and tools required for managing servers and automating workflows. It helps professionals quickly perform tasks like system monitoring, file management, networking, and process handling. With this cheatsheet, DevOps Engineers can streamline operations, troubleshoot issues efficiently, and enhance overall productivity in Linux environments.

Thumb

0 repins 0 comments

30 Powerful Cybersecurity Search Engines can help security professionals and researchers gather critical threat intelligence, track vulnerabilities, and analyze network security in real time. These specialized search engines, like Shodan, Censys, and GreyNoise, provide access to exposed devices, open ports, security misconfigurations, and emerging threats across the internet. Using these tools enhances proactive threat hunting, vulnerability assessments, and overall cybersecurity awareness for both individuals and organizations.

Thumb

0 repins 0 comments

The Windows Authentication Mechanisms & Security Tokens Cheatsheet is a quick-reference guide designed to help IT and cybersecurity professionals understand how authentication works in Windows environments. It covers key mechanisms like Kerberos, NTLM, and Smart Card logins, along with the role of security tokens in verifying identity and access. This cheatsheet simplifies complex concepts, making it easier to grasp credential handling, token types, and secure authentication flows in Windows systems.

Thumb

0 repins 0 comments

Thumb

0 repins 0 comments

Security+ Training in UAE offers foundational cybersecurity knowledge for IT professionals seeking to build or enhance their security skills. This globally recognized certification covers essential topics like network security, threat management, and risk mitigation. With growing demand for certified professionals in the Middle East, CompTIA Security+ Training in the UAE is ideal for those aiming to secure entry- to mid-level roles in cybersecurity and improve job readiness in both public and private sectors.

Thumb

0 repins 0 comments

Widely used deep learning algorithms include models like Convolutional Neural Networks (CNNs) for image processing, Recurrent Neural Networks (RNNs) for sequential data like text and time series, and Transformers, which power modern NLP tools like ChatGPT. Generative Adversarial Networks (GANs) are also popular for creating realistic synthetic data. These algorithms enable advanced applications in computer vision, speech recognition, natural language processing, and more, making them foundational to the rapid progress in artificial intelligence today.

Thumb

0 repins 0 comments

The CRISC (Certified in Risk and Information Systems Control) certification, offered by ISACA, is tailored for professionals focused on enterprise risk management and control. It validates the ability to identify, assess, and manage IT risks while implementing effective information system controls. Ideal for risk managers, control professionals, and IT auditors, CRISC demonstrates a strong understanding of how to align IT risk with business objectives. Earning CRISC enhances credibility and career prospects in risk-focused roles across industries.

Thumb

0 repins 0 comments

Free Masterclass on Crack CISM in First Attempt Date: 12 June (Thu) Time: 08:30 – 09:30 PM (IST) Speaker: Shashank Free Register Now: https://www.infosectrain.com/events/crack-cism-in-first-attempt/ ➡️ Agenda for the Masterclass • Overview of the CISM exam and four domains • Developing and implementing information security policies and standards, best practices, and alignment with business strategy • Enterprise governance and the role of information security governance • Organisational structures and roles in information security governance • Information security compliance, adhering to legal and regulatory requirements ➡️ Why Attend This Masterclass • Get CPE Certificate • Learn from Industry Experts • FREE Career Guidance & Mentorship

Thumb

0 repins 0 comments

Forget signatures—

Thumb

0 repins 0 comments

Understanding the OSI Model can be tricky, but using a simple food delivery analogy makes it easier to grasp. Just like placing an order and receiving your meal involves several steps and roles, data traveling across a network follows a layered process. Each layer of the OSI Model has a specific function—working together to ensure your message (or meal) arrives safely and accurately at its destination.

Thumb

0 repins 0 comments

Free Masterclass on Conquering CCSP: Get Exam Ready in 2 Days Date: 03 – 04 June (Tue – Wed) Time: 08:00 – 10:00 PM (IST) Speaker: Krish Free Register Now: https://www.infosectrain.com/events/fast-track-to-ccsp-success-in-2-days/ ➡️ Agenda for the Masterclass Day 01: • Decoding CCSP • Exam Mindset • Planning your exam in a month • Exploring Domains 1-3 • Practice Q&A Day 02: • Exploring Domains 4-6 • Practice Q&A

Thumb

0 repins 0 comments

Next Page